

203·
22 hours agoThese are the only bans in your mod log:
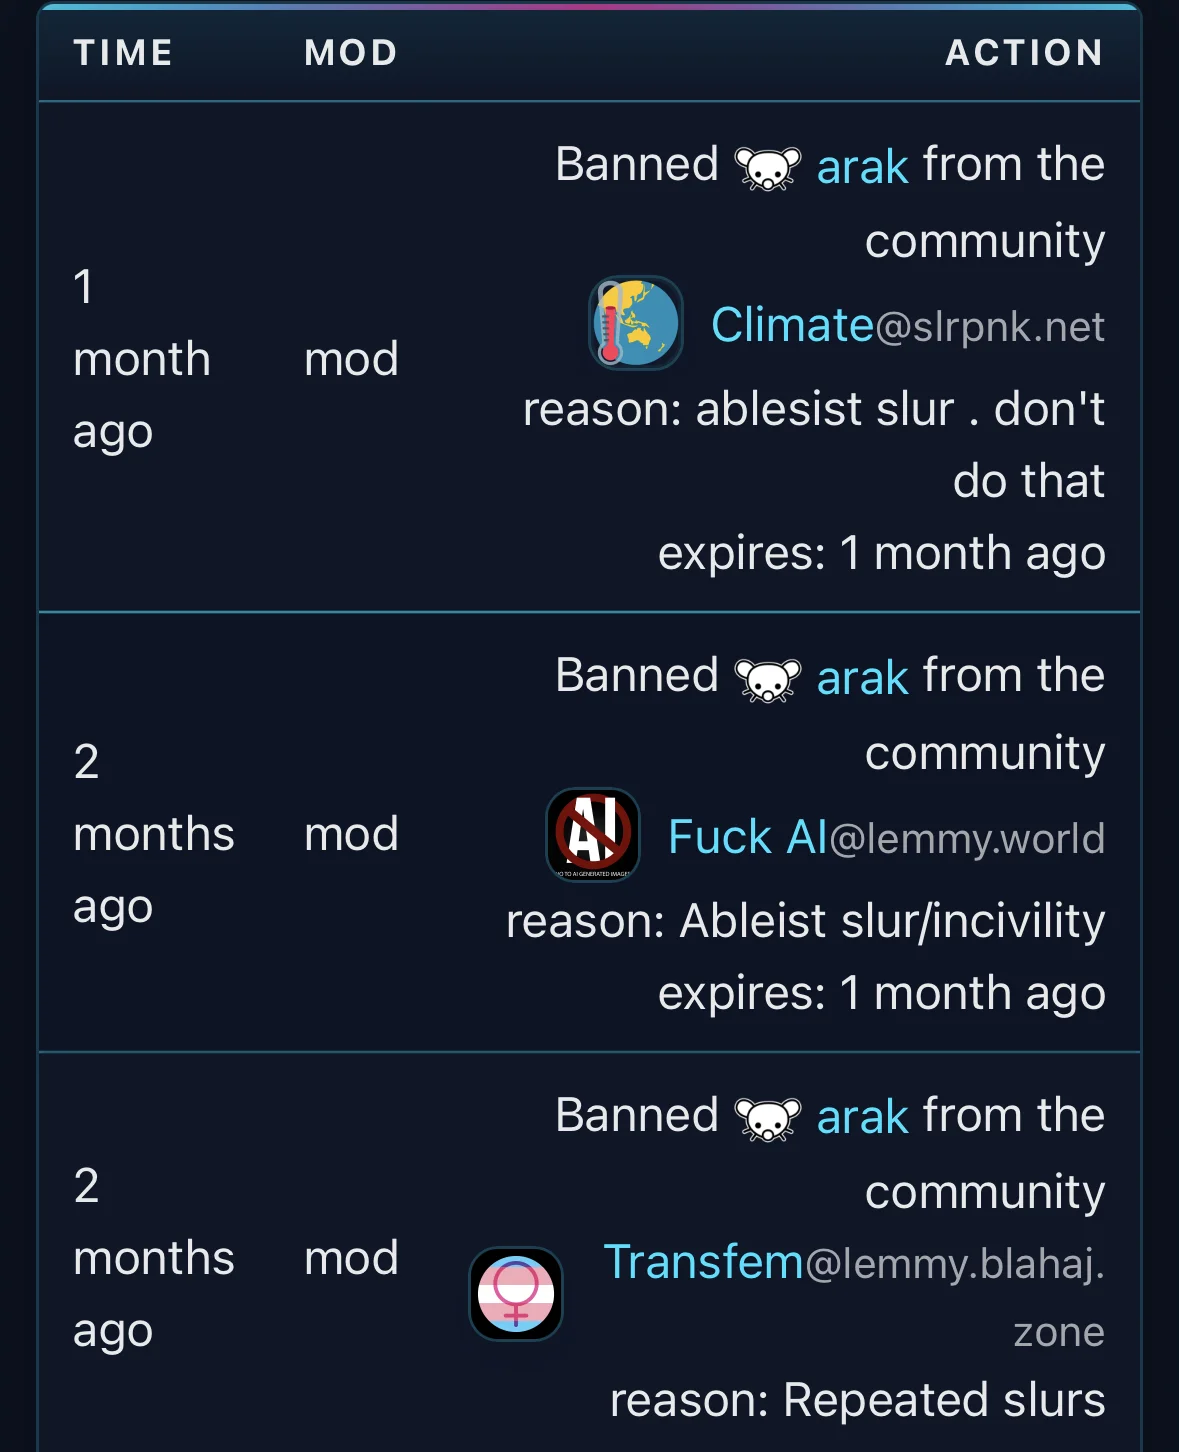
And of those three, one has already expired. Maybe stop using slurs? Because you have a lot of removed comments.
These are the only bans in your mod log:
And of those three, one has already expired. Maybe stop using slurs? Because you have a lot of removed comments.

There are already supply contracts all the way through 2027, ‘28, and most of ‘29. Even if it pops today, new supply wouldn’t start to become available until closer to 2029 at the earliest. And the price floor has permanently been raised, because the manufacturers have seen what consumers are willing to pay.
Also, it’s funny that he touts logged-out access while a large percentage of the site is walled off. They also block VPNs if you’re logged out, because they want to be able to tie your tracking data to a specific account. They can do that easily if you’re not on a VPN, so they let you browse without an account.
But if you’re behind a VPN and blocking all of their background trackers, they can’t easily tie your browsing history back to a specific user. So they force you to log in, so they can track everything your account does.
Damn, beat me to it. The Fast & The Furious truck hijacking is one of my “what part of a movie hasn’t aged well” go-to responses. They were stealing shipments full of millions of dollars of ultra high-end, top-of-the-line, super high-tech… DVD players? The same DVD players that are like $5 for an entire pallet on eBay now?
No, you don’t understand! The company said we were designing our robots to be able to hold a gun, so that it could use seed cannons to autonomously plant trees! So that it could use squirtguns to fight fires! So that it could play laser tag with children! Why would they lie about something like that?
Oh, that’s just Nanners Georg. He does that sometimes. Okay, most of the time… Okay, basically constantly. If you ask him about it, he usually just mumbles something about lizard people. We’re not even sure where he keeps getting the bananas, because nobody ever sees him near a grocery store.
Do you think “anarchy” means you actively try to give zero-day methods to state-sponsored hackers?
I mean, following proper disclosure procedure requires giving the manufacturer adequate time to patch the vulnerabilities before they are released. Would you prefer they just publish the full how-to right up front, and create a zero-day for anyone (from script kiddies to state-sponsored hackers) to use as they see fit?
“We have one full-time staff member (that’s me) and 14 mostly part-time contractors,” Executive Director Elizabeth Barron of the PHP Foundation said via email in an interview on Friday. Board members are unpaid volunteers, and funding comes from donations and grants.
Sounds more like she is stretched thin, and pointing out how unsustainable the current model is. Only one person dedicated to maintaining a programming language that ~70% of the internet uses is the perfect example of that xkcd “all modern infrastructure, vs one obscure person who has thanklessly been maintaining a project since 1997” meme.
I’m curious what you mean, because my phone has a perfectly usable file browser. By default it creates a data folder for each app, the same way Windows programs can create a directory in your user Documents folder for their data. In fact, there are some things that Apple’s file browser actually does better. For instance, the iPad has native pdf support, complete with markup, signing, combining multiple documents, etc… All available directly in the file browser.

DON’T GASLIGHT ME, JESUS!
For repeatedly driving into your thigh, just to feel something for once.
Human intervention only automatically kicks in when the car actually thinks it is trapped. Which can easily take a while for larger parking lots.
It’s really not that hard to believe. Waymo will use any available roads to navigate between fares, and it can become especially bad when they’re waiting for fares. Because they don’t just return to a home parking spot and wait between fares. The point is that they want to spread their potential reach (and ensure there are cars nearby regardless of where they’re requested) so they spread out until they need to return to charge/refuel.
They cruise around random backroads and residential areas until a fare requests them. They also avoid U-turns whenever possible, which means they’ll often path through some interesting places just to avoid turning around. They quickly clog residential roads when fares are slow, by all driving in a holding pattern around residential areas that aren’t designed for that kind of through traffic.
It doesn’t, as long as those images are good about keeping their dependencies up to date. Because containers are entirely self-sufficient and come packaged with all of their necessary dependencies, there is a potential security concern with images keeping dependencies pinned to old, insecure versions. And catching that can be tricky sometimes, especially when you’re running larger stacks with lots of containers.
But I’d argue that is actually the image being insecure, not containerization itself. It would be no different from a program being considered insecure. We would handle an insecure image the same way we would handle an insecure program: push the maintainer to update their shit to a secure version, or fork it (if it’s OSS) to update the dependencies directly.
Plus, containerization is much more straightforward compared to the olden days of directly managing dependencies. For larger setups, that was basically a full time job by itself. Especially when you have multiple different programs all trying to call different versions of the same dependency.
Their actual name is written in Cyrillic, which you can’t type with a standard QWERTY keyboard. So yeah, English speakers just use the acronym for the translated IRA instead.
Christa Pike was sentenced to death. The sentence itself was already fairly controversial, due to some of the details of her case. And now the state has attempted to kill her twice, but they keep fucking up her lethal injection. She has been injured during both attempts, but not killed. She even requested a firing line instead of a lethal injection, because she has a heart condition that will likely prevent the lethal injection from properly stopping her heart. But the state has refused to back down, and keeps injuring her with bad lethal injections instead.
I can actually confirm that dropping a piano makes the characteristic BOOOOOONG sound that we all know. I’m not sure if they actually dropped a few pianos to record it… But I have personally dropped a piano off a ~10’ drop, (and was in the room when a second piano got dropped ~6’) and it sounded exactly like what you’d expect.
All of this is to say that if they didnt drop a piano, (because that’s risky and very expensive just for a sound effect), those foley artists were really fucking good at their jobs.
Yup.
For the unaware: modern hash algorithms have character limits, but it’s nothing that would ever interfere with a regular password. Even accounting for the salt that gets appended to the end of your password before it goes into the algorithm. Most of the popular hashes have a 128 character limit, and the site will also store a salt in your user’s database entry. That salt gets appended to your password before it goes into the hash. Basically, even if two users have the same password, the hash for each will see “password{Salt1}” and “password{Salt2}”. So they won’t show as the same hash in the database, even though they’re the same password.
This salt is to prevent something called a rainbow table attack, where a hacker feeds a bunch of common passwords into a bunch of common hash algorithms, then compares with their stolen database. If they find matches, they now know which algorithm the database was using, and they only need to brute force the database once. So for instance, they feed “{common password}” into several hashing algorithms. One gives the result “1234567890”. They then check their stolen database, and find several users with the hash “1234567890”. They try using {common password} on those user accounts, and they work! Now the hacker knows which hash algorithm was used, and can brute force the entire stolen database at their leisure.
By appending a salt to each password, “{common password}” actually becomes “{common password}{Salt1}” “{common password}{Salt2}”, etc… So even if the hacker tries to brute force it, they would need to brute force each individual password instead of brute forcing the entire database all at once. It’s still important to use strong passwords, because a weak password will still be broken in only a few seconds. But that will be a few seconds per weak password, instead of a few seconds for every user at the same time. This is why sites tell you to change your password after a breach. The idea is that salting the database makes brute force attacks take a lot longer, and gives most users time to change their passwords before the attackers manage to get anything.
All of this is to say, you could have a 100 character password limit, and still have plenty of room for a 16-28 character salt. And the hashes will output the same length string regardless of what you feed into it. So longer or shorter passwords won’t matter, because they’ll all turn into a 64 character hash in the end.
So putting a low character limit on a password is a site admin tattling on themselves, because it means they’re not hashing your password at all. If they were hashing it, the only upper limit on your password would be whatever the algorithm can accept (probably 128 characters) minus 20-30 characters for a salt.
I don’t know their specific situation, but Walmart is often the only viable option for many lower population areas or late-night needs. A large part of Walmart’s expansion strategy is moving into a small town, then under-pricing all of their stuff at a loss. They keep selling things at a loss until all of the other local shops close, because they can’t compete with Walmart’s lower prices. Then once all of the local competition is run out of town, Walmart jacks their prices up because they’re the only option in town.
They’re also often one of the only grocers that stays open late. This means they’re often the only viable option for third-shift workers, because the alternative would be waking up at their equivalent of 2AM to go grocery shopping.